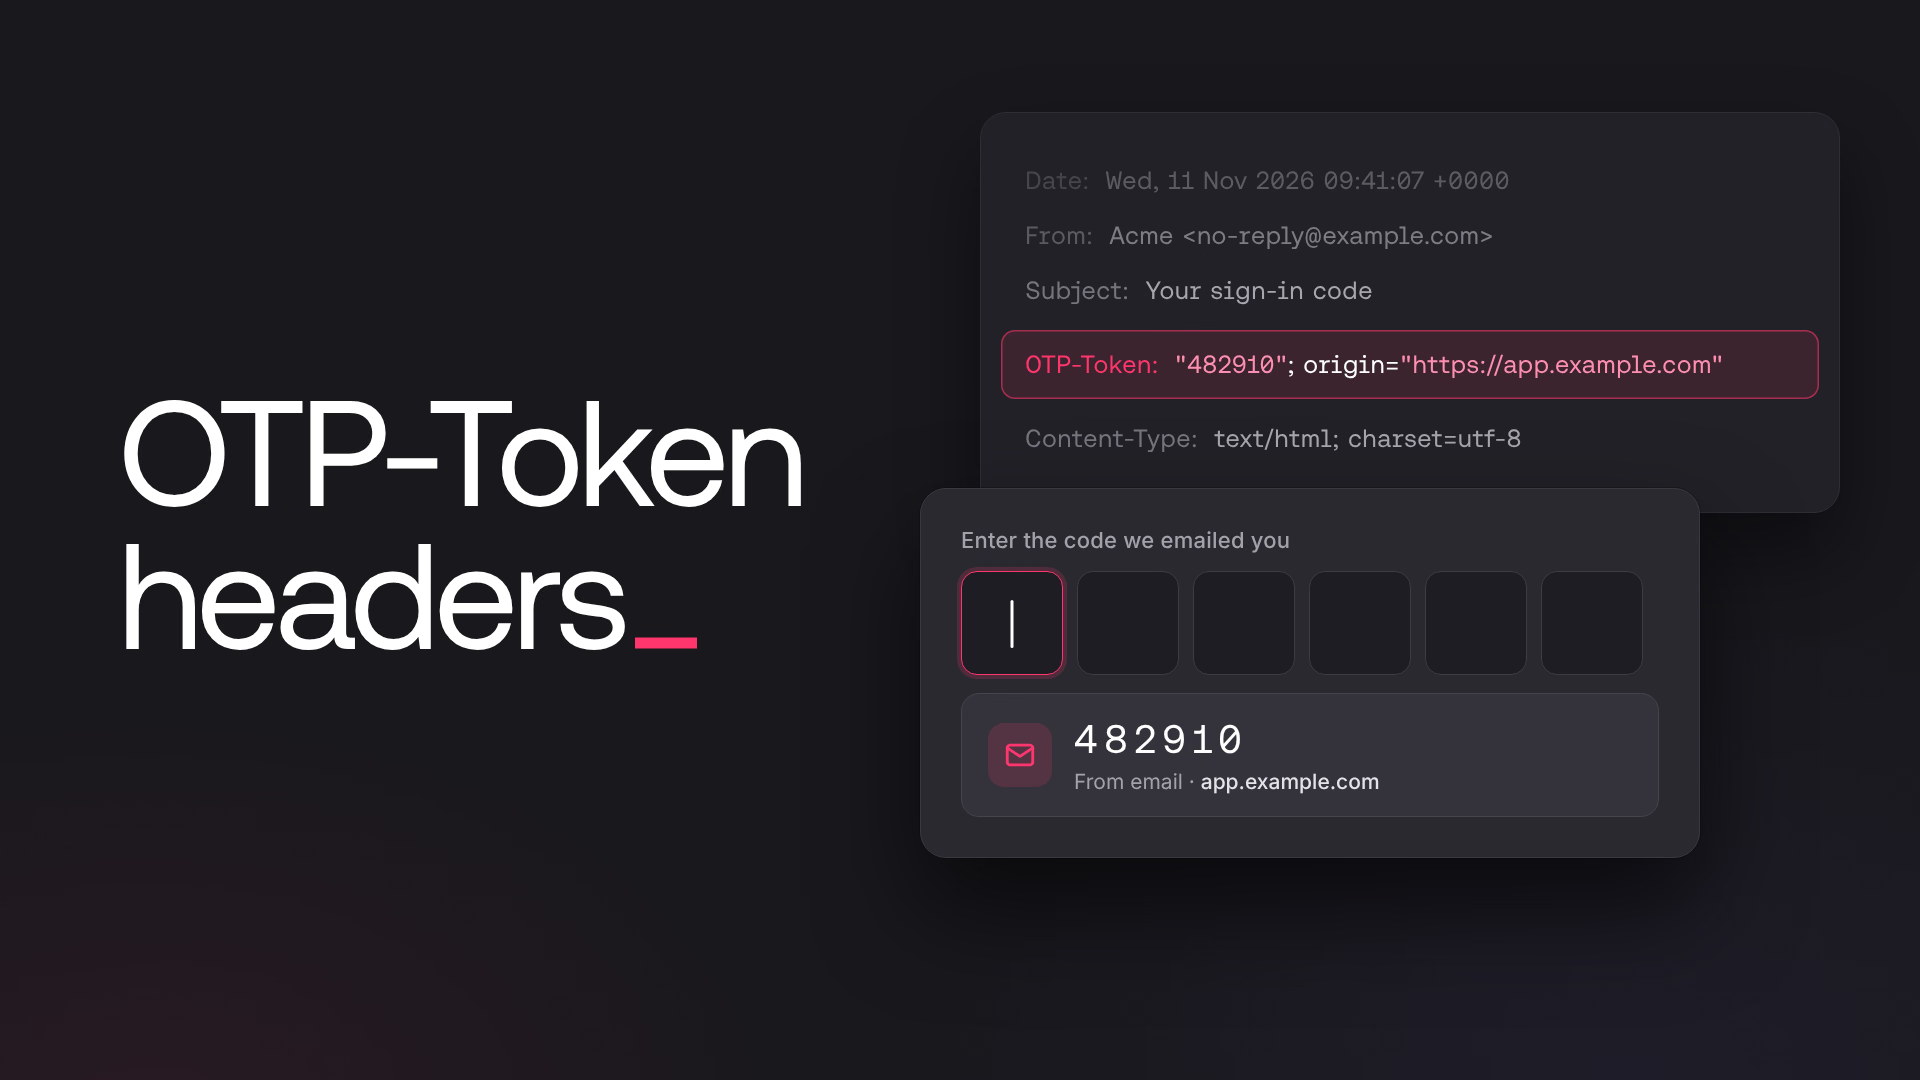
Every Appwrite Auth email that carries a one-time code now includes an OTP-Token header that binds the code to the origin that requested it:
OTP-Token: "123456"; origin="https://app.example.com"The header comes from the OTP-Token Internet-Draft. Mail clients, browsers, and password managers that support it can autofill the code on your app's origin and nowhere else. Appwrite adds it to email OTP sign-in, email verification codes, password recovery codes, and MFA email challenges. Appwrite adds it only for HTTPS origins and local development hosts, so server SDK calls and native apps get the same email as before.
There's nothing to configure. Mark your code inputs with autocomplete="one-time-code" so browsers know where the code belongs. The header is also available in self-hosted Appwrite 2.7 and later.